Next.jsReactTypeScriptSupabaseStripeClaude APIVitestVercel
August 16, 2026Mako
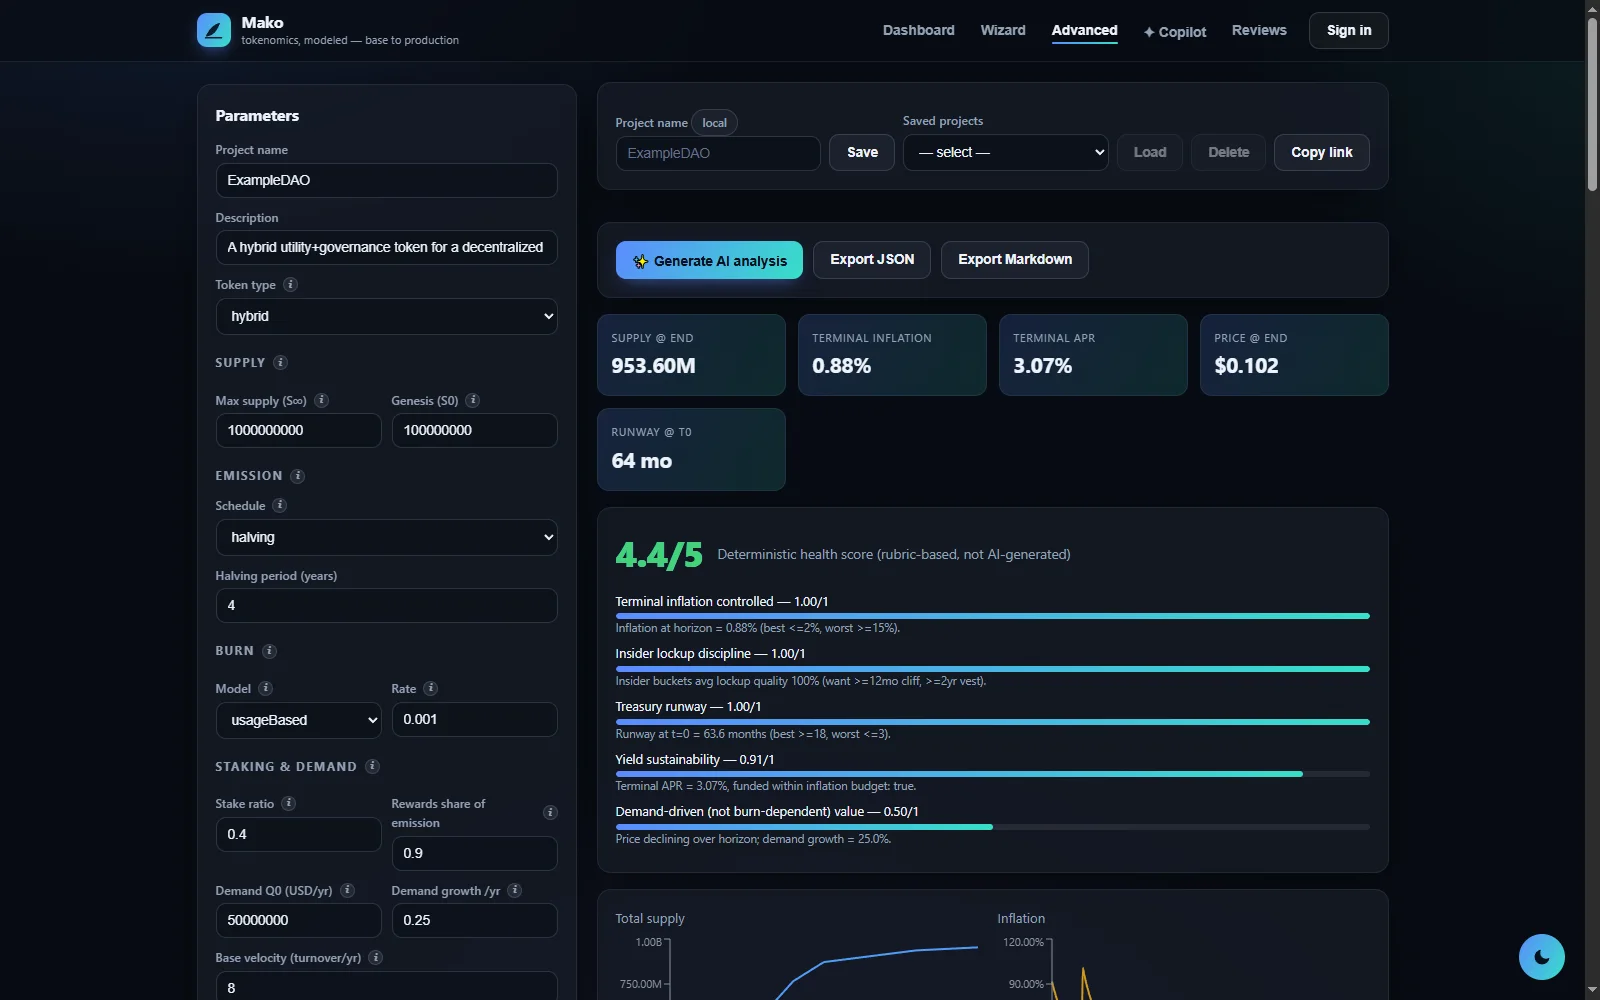
Mako models a crypto token’s economics with real math and reproducible numbers, then adds an AI strategy analysis that is grounded in those numbers. The model writes prose around figures the engine produced. It never invents them.
The engine
A pure TypeScript simulation with no framework dependencies, covered by unit tests:
- Supply, emission and burn as an ODE, plus cliff-and-linear vesting, inflation, staking APR and treasury runway.
- A corrected equation-of-exchange price model,
P(t) = Q(t) / (V_eff(t) · S(t)). The template this started from had the Fisher equation inverted. - Monte Carlo risk: seeded jump-diffusion around the price path, with p5/p50/p95 fan charts and a VaR table.
- Quadratic vs one-token-one-vote governance concentration, a multi-asset treasury, Bear/Base/Bull scenarios, an AMM with a bonding curve, and a Howey-test regulatory heuristic.
- A 0–5 health score, plus JSON and Markdown export.
Charts and tables run locally in the browser, so manual modelling costs nothing and works offline.
The AI copilot
- Claude tool-use loop: you chat in plain language. The model calls
update_params(Zod-validated) andget_analysis(which runs the engine), so it reasons on real numbers. - Control mode proposes a diff you apply or reject. Full mode applies it automatically, with undo.
- The LLM sits behind a provider interface. Anthropic is the default and OpenRouter is a drop-in alternative.
SaaS and security
- Supabase auth and project sync, with Row-Level Security on every table.
- Stripe plans, top-ups and webhooks. Tokens are converted to credits and deducted atomically in a locked-down Postgres function, with daily and weekly caps so a burst can’t drain the monthly budget.
- Secrets live only on the server, and the build fails if one leaks into client code. Every request is Zod-validated and each IP is rate-limited.
- User text is fenced as untrusted input in the prompt, and model output passes through
rehype-sanitize. - Strict CSP, HSTS and frame-deny headers.
npm auditreports 0 vulnerabilities. - Built with Next.js 16 and React 19, and packaged for Vercel.